SECURITY & COMPLIANCE, CONNECTED
Compliance is only the beginning.
SecureC brings compliance readiness, security testing, continuous monitoring and workforce training into one connected ecosystem—engineered in India for businesses worldwide.
Designed for teams working toward ISO 27001, SOC 2, HIPAA, PCI DSS, GDPR, DPDP and stronger security operations.
Built for the standards your customers ask about
- ISO 27001
- SOC 2
- HIPAA
- PCI DSS
- GDPR
- DPDP
Move from scattered work to one security posture
Policies live in documents. Evidence lives in inboxes. Vulnerabilities sit in reports. Alerts arrive in separate tools. Training records remain disconnected.
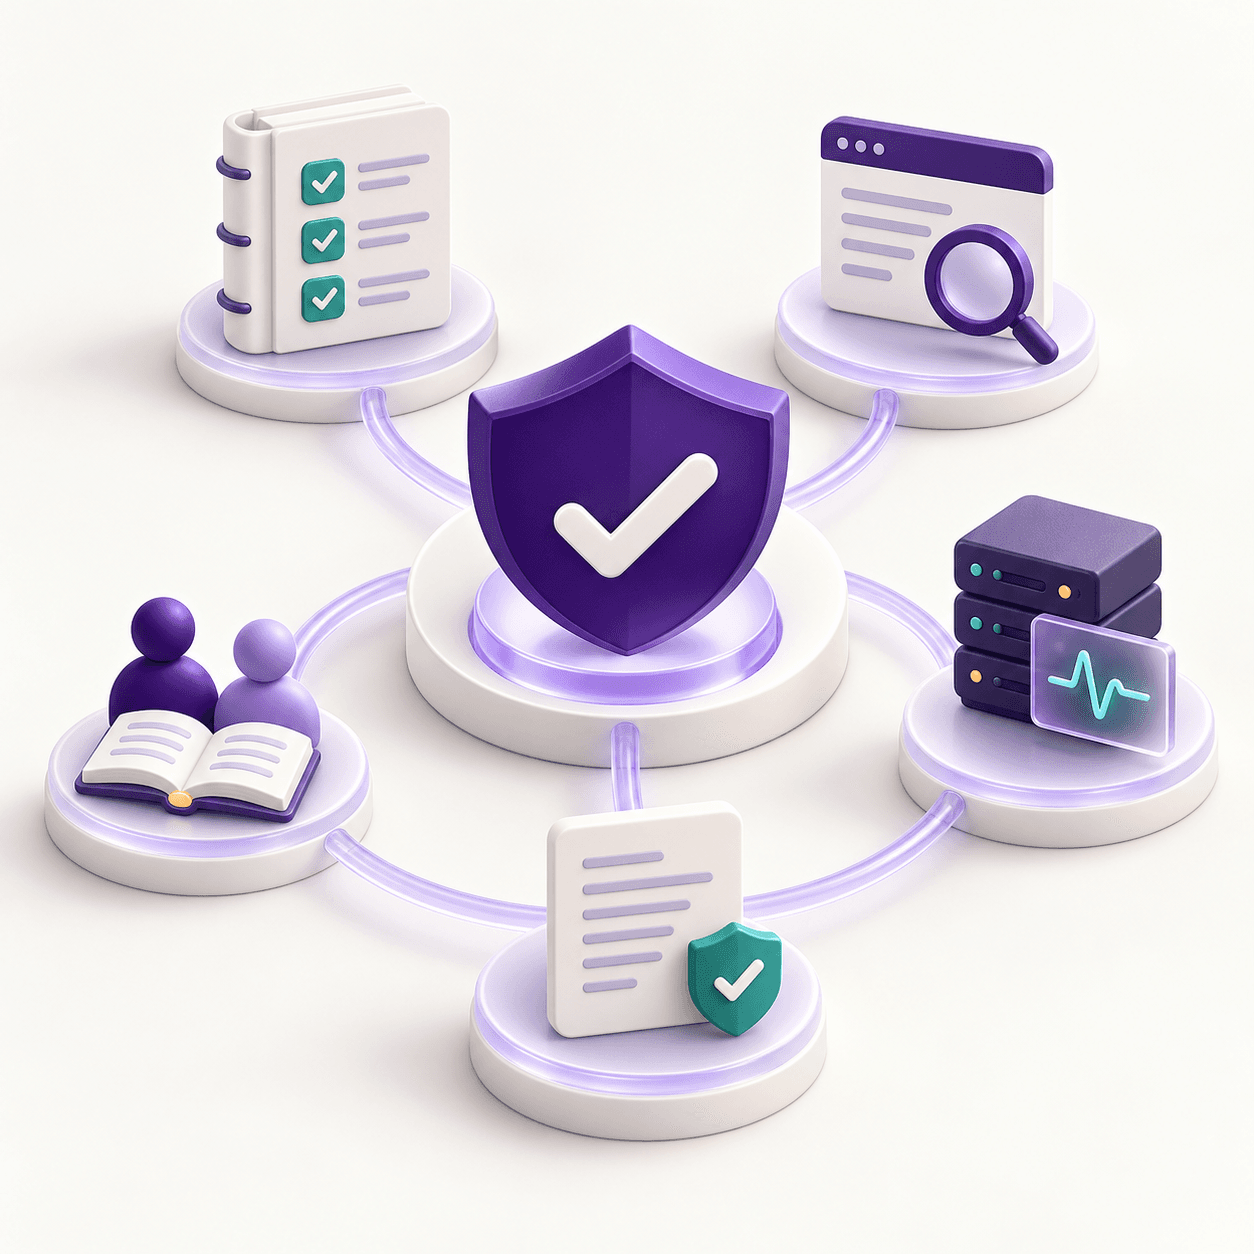
SecureC connects these activities so leaders can see what is compliant, what is exposed, what needs action and what can be proven to customers.
Comply continuously.
Organize controls, policies, evidence, owners and audit preparation.
Test what matters.
Assess applications, APIs, mobile products, cloud infrastructure and networks.
Detect meaningful threats.
Prioritize security signals and coordinate investigation and response.
Strengthen your workforce.
Deliver awareness, phishing and role-based security training.
THE PROGRAM PATH
Start with compliance. Expand into resilience.
- Step 01
Assess
Understand scope, obligations and current gaps.
- Step 02
Comply
Implement controls and collect defensible evidence.
- Step 03
Validate
Test whether technical safeguards work in practice.
- Step 04
Monitor
Watch for meaningful security events and control drift.
- Step 05
Educate
Reduce human risk and track completion.
- Step 06
Improve
Close gaps and keep the program current after the audit.
ONE CONNECTED SYSTEM
One ecosystem, four focused capabilities
SecureC Comply
Run compliance as an operating process, not a document hunt.
- Controls mapped across the frameworks you need
- Policies, owners and review cycles in one place
- Evidence collected with its source and validity
SecureC Assess
Find out whether your safeguards hold up in practice.
- Web, API and mobile application testing
- Cloud and network configuration assessment
- Retesting that confirms fixes actually landed
SecureC Defend
Spend analyst attention on the signals that matter.
- Security event collection and correlation
- Prioritized detections with investigation state
- Coordinated incident and response workflows
SecureC Academy
Reduce human risk and be able to show it.
- Security awareness for every employee
- Phishing simulation with reporting practice
- Role-based and secure development training
FRAMEWORK COVERAGE
Global frameworks. Practical guidance.
ISO 27001
GlobalBuild an information security management system and prepare for independent certification.
SOC 2
US buyersPrepare for a Type I or Type II examination against the trust services criteria.
HIPAA
US healthcareOrganize safeguards and documentation for protected health information.
PCI DSS
PaymentsScope cardholder data environments and evidence the required controls.
GDPR
EU/UKConnect data protection obligations to the controls that support them.
India: DPDP & CERT-In
IndiaPrepare for DPDP obligations and CERT-In audit expectations together.
INDIA TO THE WORLD
Built in India for global business
See where your security and compliance program stands.
Send us a few details and the SecureC team will get back to you to talk through your scope, obligations and the practical next step.
QUESTIONS
Before you start
Is SecureC a certification body?
Can we begin with only one service?
Does using SecureC guarantee compliance?
Explore the ecosystem
- How the platform connects
One system across compliance, testing, monitoring and training.
- Compliance readiness
Controls, policies, evidence and audit preparation.
- VAPT and security testing
Application, API, mobile, cloud and network assessment.
- SOC monitoring
Detection, prioritization and incident workflows.
- Security training
Awareness, phishing simulation and role-based learning.
- Framework coverage
Route by the standard your customers or regulators expect.