THE SECUREC PLATFORM
One view of security. One system for action.
THE CONNECTED POSTURE MODEL
Every requirement resolves to something you can operate
- 01
Framework
The obligation you are held to
- 02
Control
What you operate to meet it
- 03
Evidence / test
Proof it works, collected or measured
- 04
Finding
Where practice and intent diverge
- 05
Remediation
The owned change that closes the gap
- 06
Trust proof
What a customer can be shown
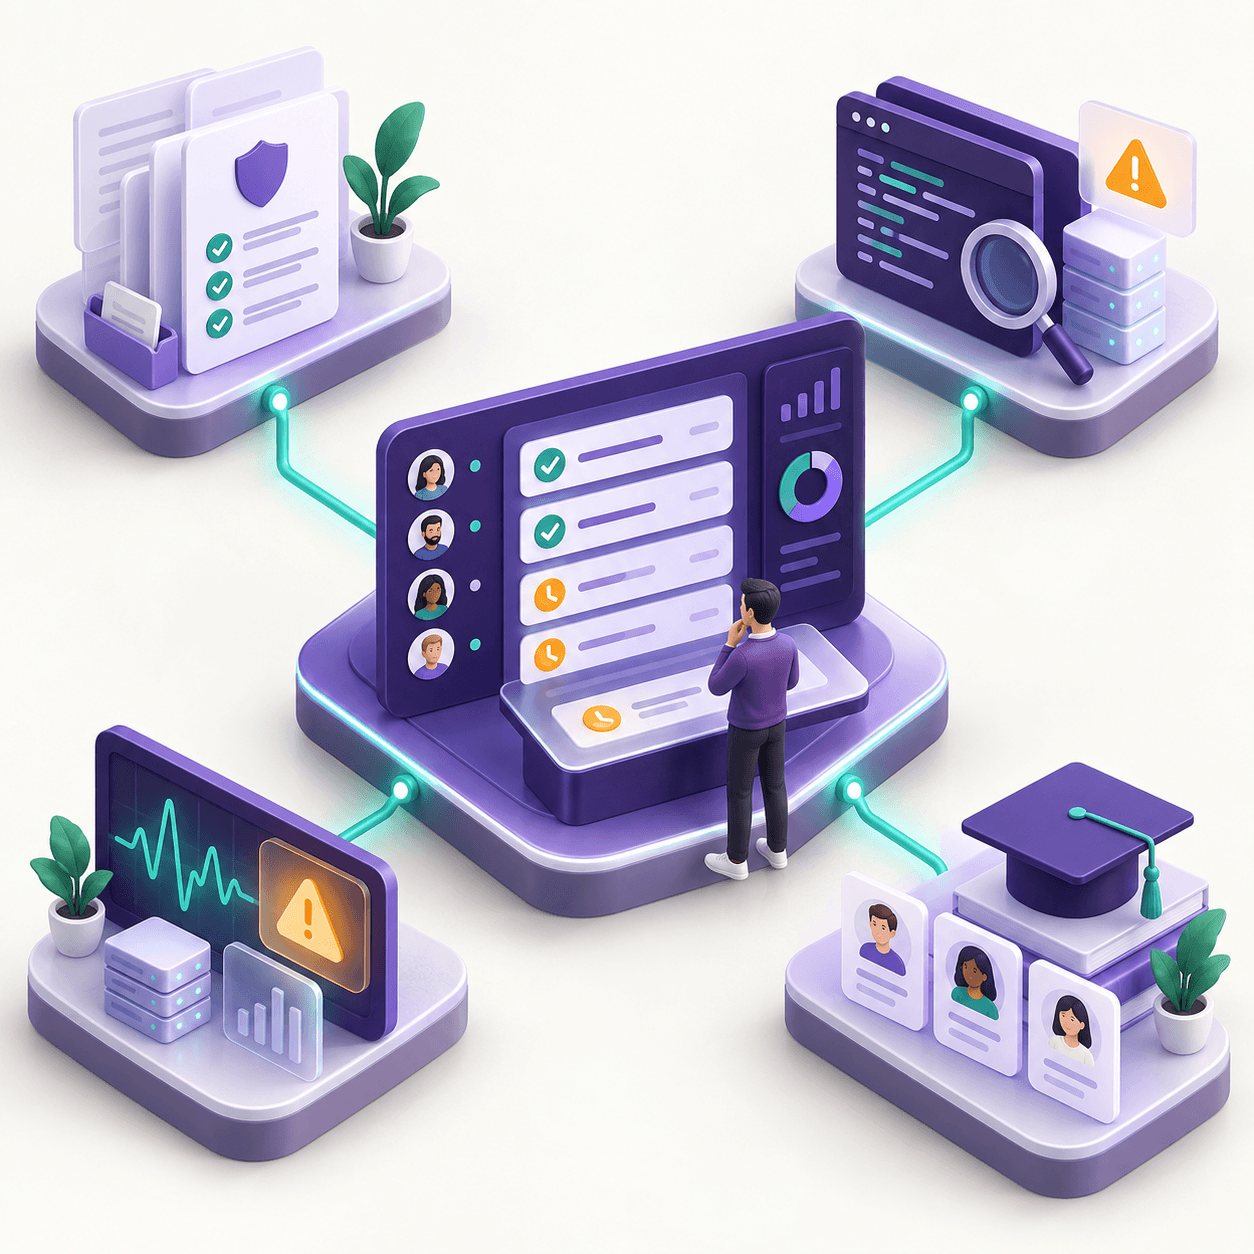
VAPT findings, security incidents and training records feed the same model, so they can support or challenge the control posture rather than sit beside it.
CAPABILITIES
Four connected workspaces
COMPLIANCE WORKSPACE
Manage the program, not the paperwork
Manage frameworks, common controls, policies, evidence, owners, exceptions and audit requests.
- One control model reused across multiple frameworks
- Policies with owners, review cycles and acknowledgements
- Evidence that keeps its source, timestamp and approver
- Exceptions and audit requests tracked in the open
| Annex | Control category | Implemented | Progress | State |
|---|---|---|---|---|
| A.5 | Organizational controls | 31 of 37 | 84% | In progress |
| A.6 | People controls | 7 of 8 | 88% | Ready for review |
| A.7 | Physical controls | 9 of 14 | 64% | In progress |
| A.8 | Technological controls | 22 of 34 | 65% | Gaps identified |
- Example ISO 27001 Annex A control categories with implementation progress and review state.
A.5
Organizational controls
- Implemented
- 31 of 37
- Progress
- 84%
- State
- In progress
A.6
People controls
- Implemented
- 7 of 8
- Progress
- 88%
- State
- Ready for review
A.7
Physical controls
- Implemented
- 9 of 14
- Progress
- 64%
- State
- In progress
A.8
Technological controls
- Implemented
- 22 of 34
- Progress
- 65%
- State
- Gaps identified
Mapped controls reuse approved evidence where requirements overlap. Scope and interpretation stay specific to each framework.
SECURITY VALIDATION
Test results land where the work happens
Bring verified VAPT findings into the same remediation view as compliance gaps.
- Findings carry severity, affected surface and an owner
- Remediation tracked alongside control gaps, not separately
- Retest outcomes recorded against the original finding
| ID | Finding | Surface | Severity | State |
|---|---|---|---|---|
| VA-2041 | Stored XSS in customer note field | Web application | High | Retest passed |
| VA-2044 | Missing authorization check on export endpoint | API | High | Fix in progress |
| VA-2049 | Session token retained after sign-out | Mobile (Android) | Medium | Awaiting retest |
| VA-2052 | Overly permissive storage bucket policy | Cloud | Medium | Fix in progress |
| VA-2057 | Verbose error messages disclose stack traces | Web application | Low | Accepted risk |
- Example penetration-test findings with surface, severity and remediation state.
VA-2041
Stored XSS in customer note field
- Surface
- Web application
- Severity
- High
- State
- Retest passed
VA-2044
Missing authorization check on export endpoint
- Surface
- API
- Severity
- High
- State
- Fix in progress
VA-2049
Session token retained after sign-out
- Surface
- Mobile (Android)
- Severity
- Medium
- State
- Awaiting retest
VA-2052
Overly permissive storage bucket policy
- Surface
- Cloud
- Severity
- Medium
- State
- Fix in progress
VA-2057
Verbose error messages disclose stack traces
- Surface
- Web application
- Severity
- Low
- State
- Accepted risk
Each finding carries reproduction steps, affected components and a remediation owner. Severity reflects exploitability and impact in context.
CONTINUOUS MONITORING
Signals that deserve a decision
Surface relevant security signals and operational evidence without presenting every log as an executive risk.
- Correlation before escalation, so routine events stay routine
- Investigation state visible with its reasoning and owner
- Control drift surfaced as an operational signal
Signals ingested
1.2M
Last 24 hours
Raised to analysts
18
After correlation
Open investigations
3
1 high severity
| ID | Signal | Source | Severity | State |
|---|---|---|---|---|
| AL-8812 | Impossible travel on privileged account | Identity provider | High | Under investigation |
| AL-8815 | New IAM role granted outside change window | Cloud audit log | Medium | Confirmed change |
| AL-8819 | Endpoint detection quarantined a script | Endpoint agent | Medium | Contained |
| AL-8823 | Repeated failed logins from one range | Application gateway | Low | Suppressed — known scanner |
- Example alert queue with source, severity and investigation state.
AL-8812
Impossible travel on privileged account
- Source
- Identity provider
- Severity
- High
- State
- Under investigation
AL-8815
New IAM role granted outside change window
- Source
- Cloud audit log
- Severity
- Medium
- State
- Confirmed change
AL-8819
Endpoint detection quarantined a script
- Source
- Endpoint agent
- Severity
- Medium
- State
- Contained
AL-8823
Repeated failed logins from one range
- Source
- Application gateway
- Severity
- Low
- State
- Suppressed — known scanner
Routine events stay muted so analysts work the signals that matter. Every state change keeps its reasoning and owner.
WORKFORCE ASSURANCE
Training that counts as evidence
Track training, acknowledgements and simulations as both risk signals and audit evidence.
- Completion recorded per person, role and course
- Phishing simulation outcomes kept in context
- Acknowledgements linked to the policies they cover
Course completion
- Security awareness essentialsAll staffOn track91%
- Secure coding for web servicesEngineeringOn track74%
- Handling customer dataSupport and salesOn track88%
- Incident reportingAll staffFollow up63%
Latest phishing simulation
- Campaign
- Invoice request — May 2026
- Recipients
- 214
- Reported to security
- 168
- Clicked link
- 19
- Submitted credentials
- 2
Completion records connect to compliance evidence, so training can be shown as an operating control rather than a spreadsheet.
What makes this different
Category conventions are easy to copy. These are the choices that change how the work actually runs.
- Security operations connected to compliance evidence
- Monitoring and testing feed the same control model that your audit evidence comes from.
- One control model across multiple frameworks
- Shared requirements reuse approved evidence, while each framework keeps its own scope and interpretation.
- Platform plus expert-led services
- Tooling where automation helps, and practitioners where judgement is required.
- India-specific requirements alongside global frameworks
- DPDP and CERT-In expectations are treated as first-class, not an afterthought.
- Designed for growing teams
- Usable by a small security function, not only by a large GRC department.
Replace fragmented security work with a connected operating model.
Start with a readiness assessment and we will map the workstreams that matter for your scope, obligations and timeline.
Go deeper
- Compliance readiness
Controls, policies, evidence and audit preparation.
- VAPT and security testing
Application, API, mobile, cloud and network assessment.
- SOC monitoring
Detection, prioritization and incident workflows.
- Security training
Awareness, phishing simulation and role-based learning.
- Framework coverage
ISO 27001, SOC 2, HIPAA, PCI DSS, GDPR and India requirements.
- Contact Us to Get Started
Tell us what customers, auditors or regulators are asking for.
- How SecureC secures itself
Our own controls, disclosure process and security contact.